Identity
Active DirectoryMicrosoft Entra IDOktaLDAPRADIUSSAML 2.0
Zones, app control, threat prevention, TLS inspection, VPN and SD-WAN in one product, all managed from one console. Here's how each part works.
Every NXSgate policy starts with zones. Put interfaces, VLANs, VPN tunnels and cloud subnets into zones that match how your network is actually used, then decide exactly what's allowed to cross between them.
| Zone | Members | Trust |
|---|---|---|
| WAN | eth0, eth1 · ISP-1, ISP-2 | Untrusted |
| LAN | vlan10, vlan20 | Trusted |
| DMZ | vlan30 · web-01, web-02 | Restricted |
| Guest | vlan40 · Wi-Fi "Guest" | Untrusted |
| IoT | vlan50 · cameras, sensors | Restricted |
| VPN | ipsec-branch-*, ssl-vpn | Trusted |
A port number doesn't tell you what's really going on. NXSgate recognizes the app itself, even when it hops ports, hides inside HTTPS or tries to dodge detection, so your rules match what people actually do.
| Application | Category | Risk | Action |
|---|---|---|---|
| MMicrosoft 365 | Productivity | Allowed | |
| ZZoom | Collaboration | Allowed | |
| CChatGPT | Generative AI | No uploads | |
| DDropbox (personal) | File sharing | Blocked | |
| BBitTorrent | Peer-to-peer | Blocked |
All the prevention engines share one decoded stream, so you can leave every one of them switched on. When something new shows up, NXSgate analyzes it and turns the result into protection for every gateway.
Most web traffic is encrypted now, and attackers count on that. NXSgate decrypts and inspects TLS where it matters, and your policy decides what stays private.
Run your WAN and remote access on the same gateway that handles security. Every path gets inspected, and every tunnel follows the same rules.
One console for every gateway, with the reports your security team needs and the APIs your platform team expects.
# LAN → WAN: allow Finance to reach its SaaS apps, fully inspected
resource "nxsgate_security_rule" "finance_saas" {
  name        = "Finance SaaS"
  from_zone   = "LAN"
  to_zone     = "WAN"
  source      = ["group:Finance"]
  application = ["salesforce", "netsuite"]
  action      = "allow"
  profile     = nxsgate_profile.strict.id
  log         = true
}

resource "nxsgate_commit" "global" {
  scope       = "all-gateways"
  depends_on  = [nxsgate_security_rule.finance_saas]
}Every model runs the same software and is managed from the same console, so your policy goes wherever your network grows.
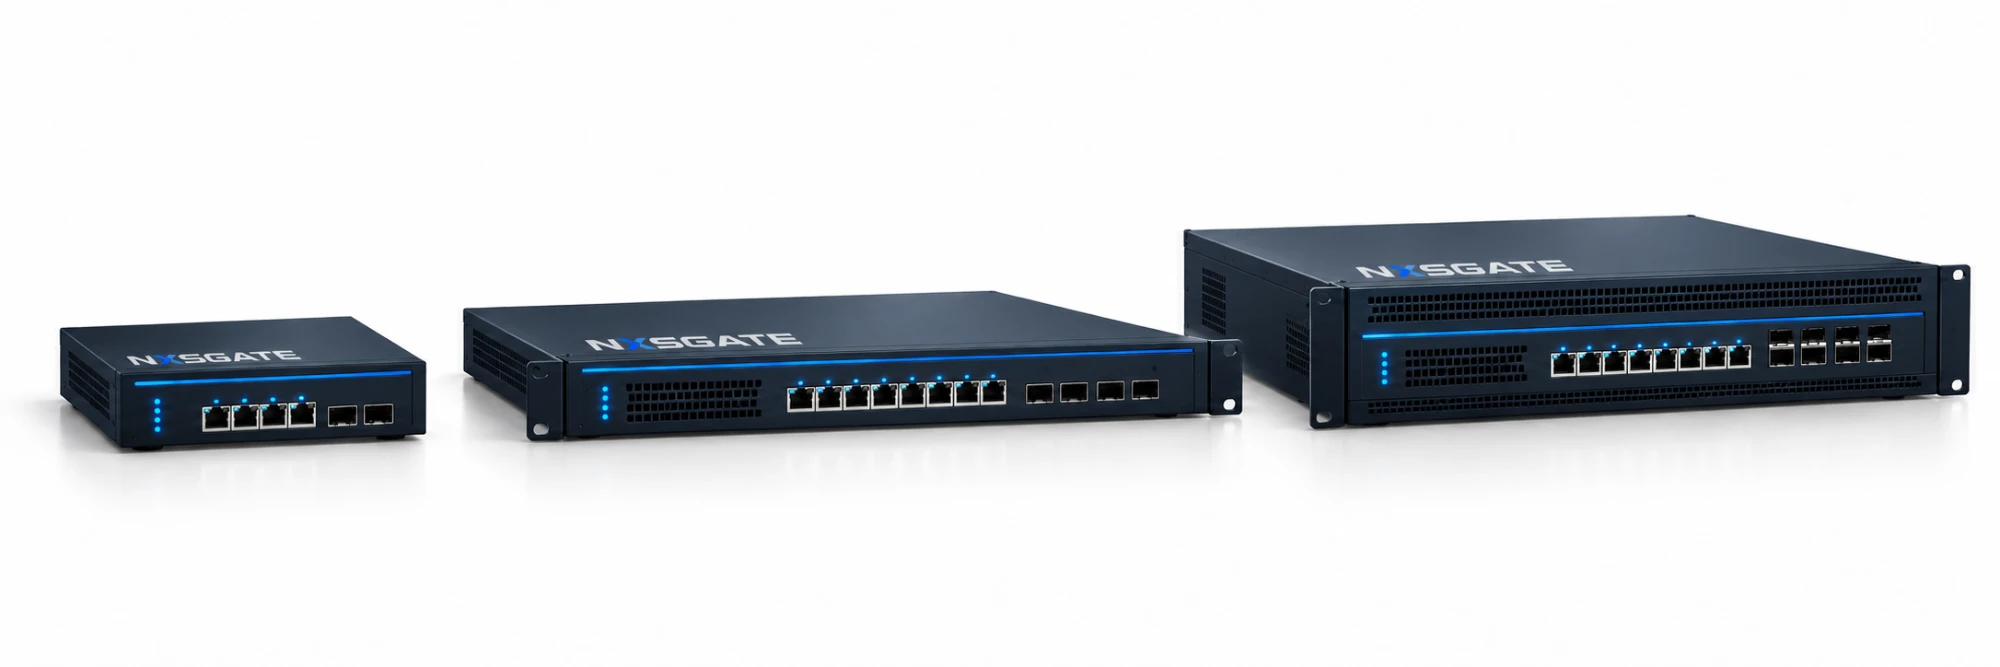
Swipe sideways to see every model.
| Specification | NXS-100Branch & small office | NXS-500Mid-size & campus | NXS-2000Large enterprise | NXS-5000Data center | NXS-VVirtual & cloud |
|---|---|---|---|---|---|
| Form factor | Desktop | 1U rackmount | 1U rackmount | 2U rackmount | VM / cloud image |
| Firewall throughput | 4 Gbps | 12 Gbps | 40 Gbps | 120 Gbps | Up to 20 Gbps |
| Threat prevention throughput | 1.2 Gbps | 4 Gbps | 14 Gbps | 45 Gbps | Up to 8 Gbps |
| IPsec VPN throughput | 1.5 Gbps | 5 Gbps | 18 Gbps | 60 Gbps | Up to 10 Gbps |
| Concurrent sessions | 500K | 2M | 8M | 32M | Up to 4M |
| Interfaces | 8 × 1GbE | 16 × 1GbE 4 × 10GbE SFP+ | 8 × 10GbE SFP+ 4 × 25GbE SFP28 | 16 × 25GbE SFP28 4 × 100GbE QSFP28 | Up to 16 vNICs |
| High availability | Active/passive | A/P, A/A | A/P, A/A | A/P, A/A, clustering | A/P, A/A |
Throughput numbers are lab estimates. Ask for the full datasheets to see how we test.
Share identity, logs and threat intel with the systems your teams rely on.
We're letting a small group of organizations try NXSgate before launch. Run it on your own network and see exactly which apps, users and threats are crossing it.